API-Connected GPTs
Connecting an AI assistant to company data is easy. Making sure it cannot leak confidential records, overwrite live databases, or execute unvetted changes is where most implementations fail. We build zero-trust edge gateways that keep your data intact.
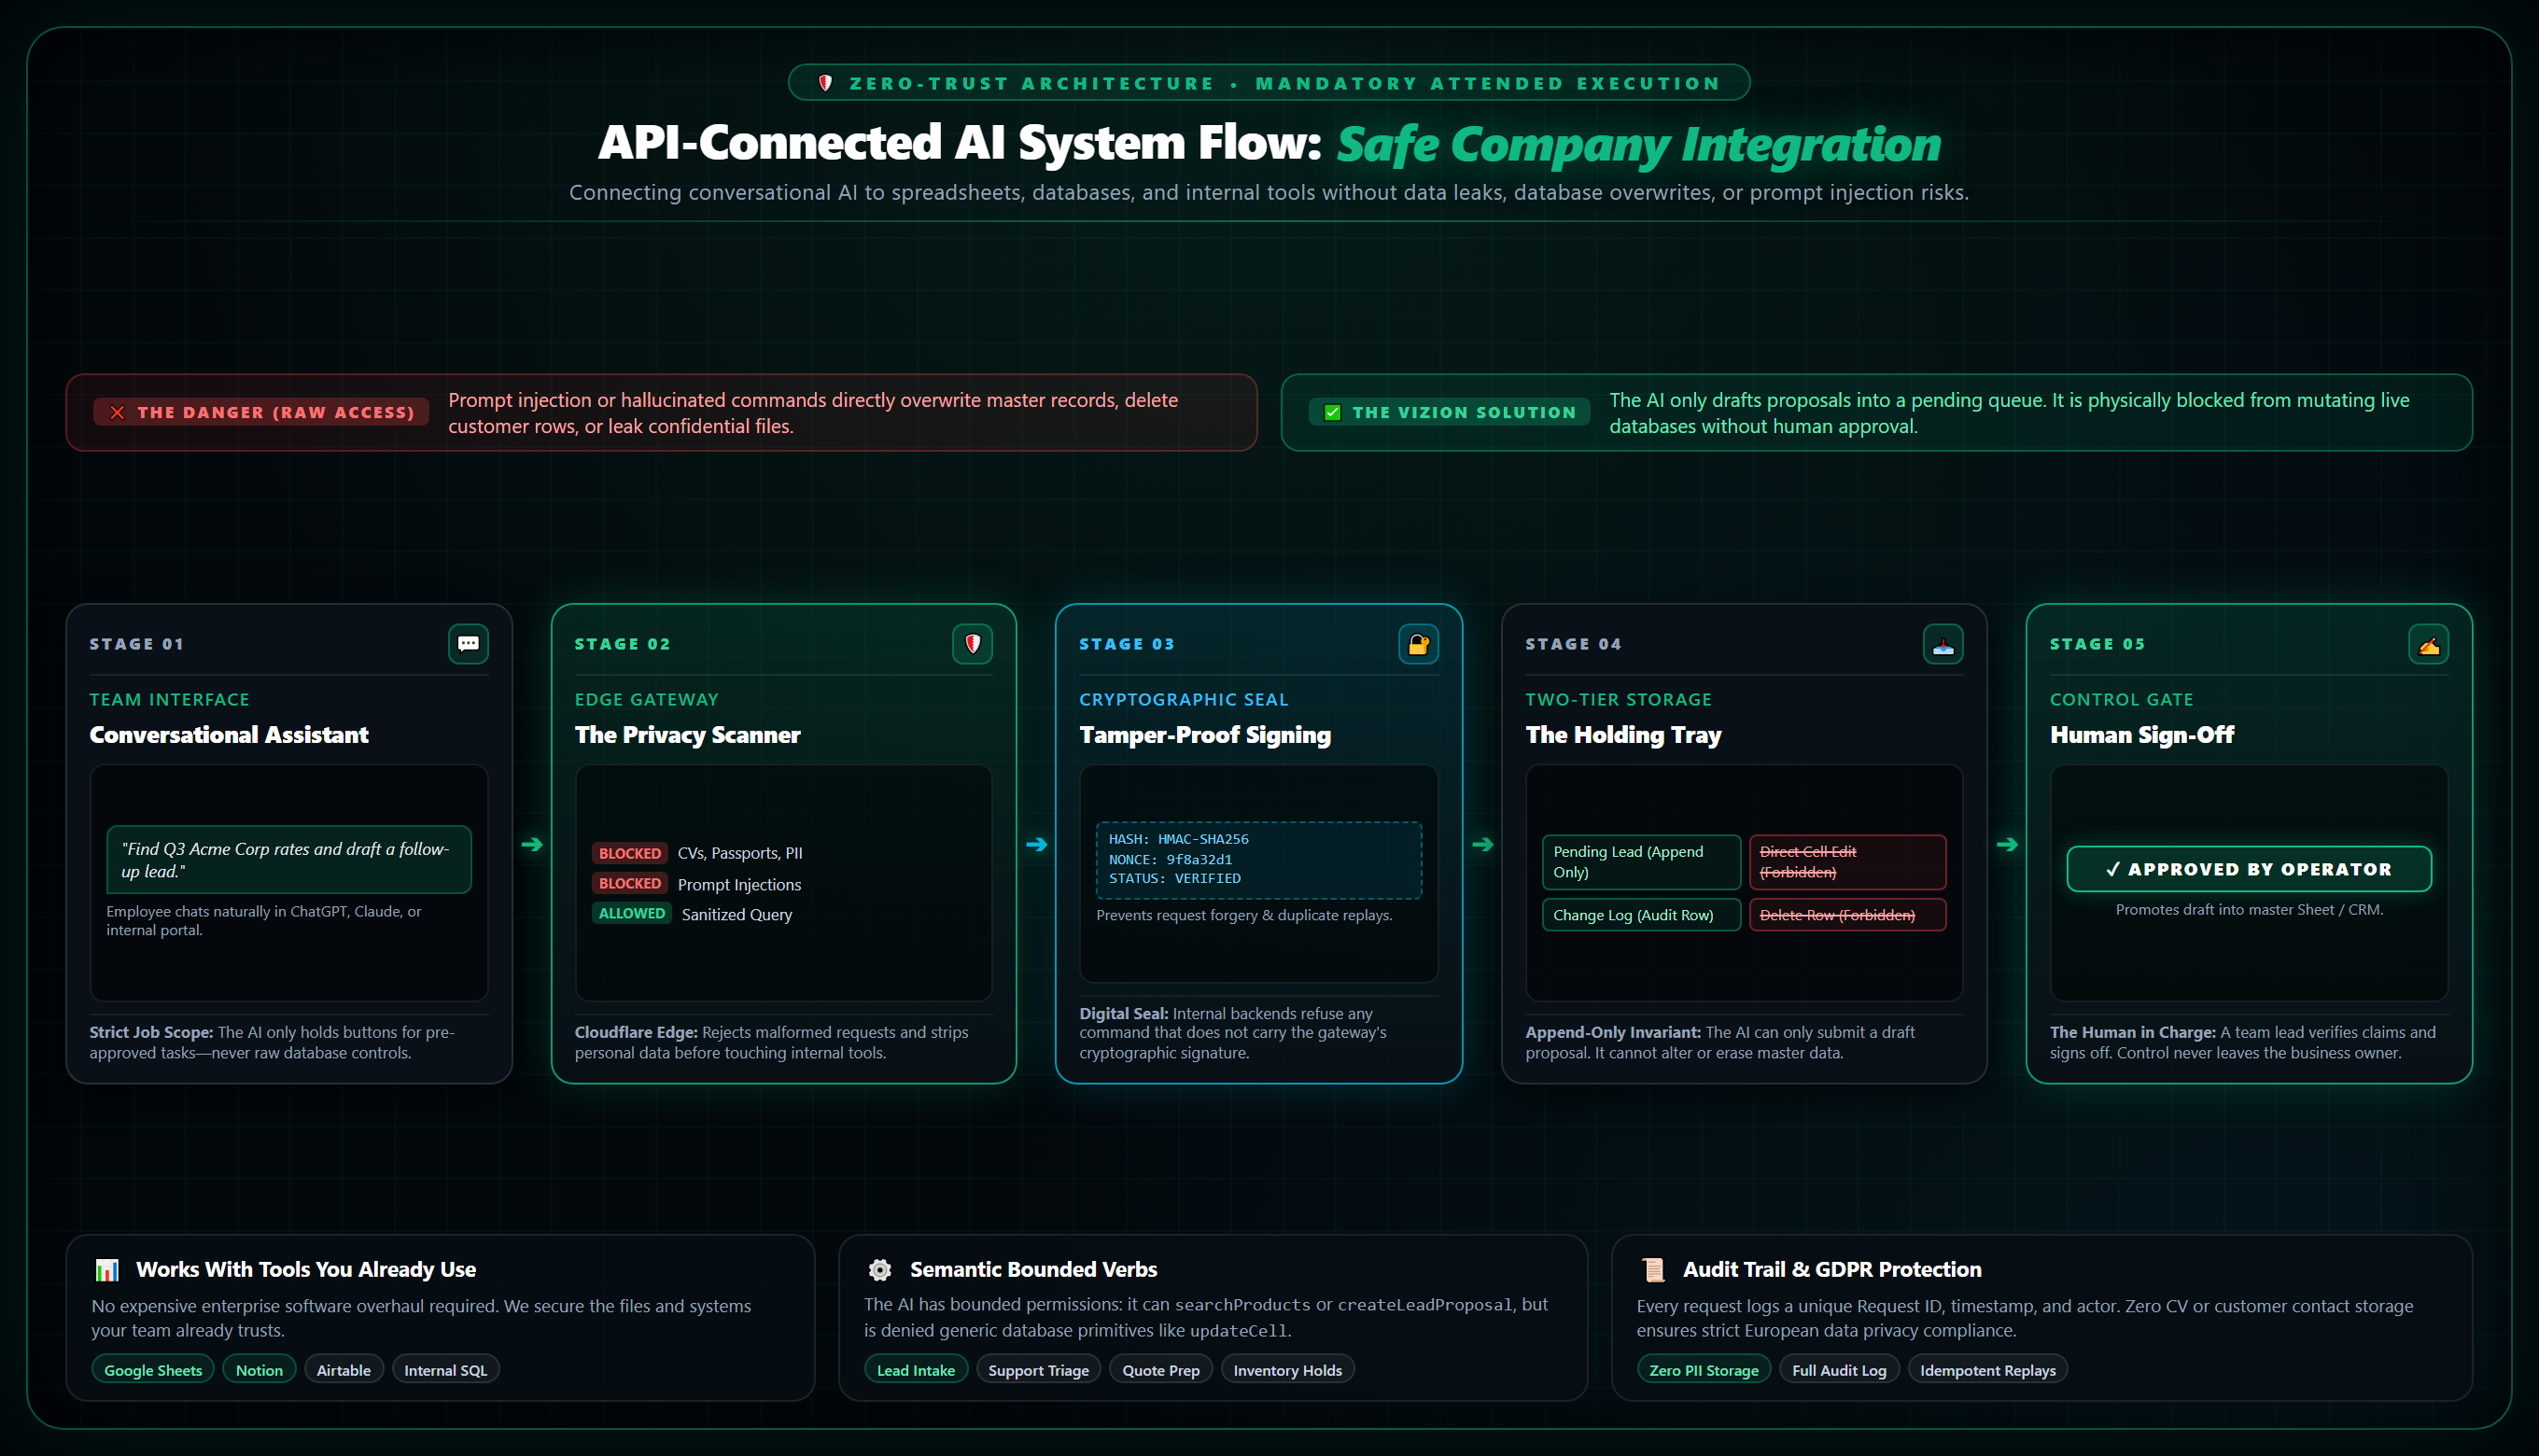
System Architecture & Flow
Starting Baseline Setup & Maintenance
Starting at 10,000 CZK setup · 10,000 CZK / mo
(approx. €420 setup · €420 / mo baseline)
The setup fee covers designing the edge gateway, defining strict OpenAPI 3.1 action schemas, configuring bearer security and HMAC verification, and connecting a secure read or proposal workflow to your database or spreadsheets.
Live integrations break as APIs evolve. Monthly maintenance covers endpoint version updates, monitoring token usage and response latencies, security certificate and credential rotation, and continuous testing to ensure prompt changes never bypass data boundary rules.
Final scope depends on the number of connected endpoints, database write permissions, and user seats. We clarify the exact scope during discovery before any commitment.
See the Czechia Expat Job Scout, our public working proof demonstrating zero CV storage, HMAC request signing, and bounded discovery queues.
The Real Problem
Prompt rules are not a security perimeter. Instructing an LLM “do not edit column C” or “keep this confidential” is wishful thinking. Prompt injections, hallucinations, or naive user inputs easily bypass conversational guidelines.
The Semantic Stance
Enforce business operations at the gateway. The LLM is never granted generic primitives like updateCell, deleteRow, or executeQuery. It can only call bounded semantic verbs like searchRecords or submitDiscoveryProposal.
What It Proves
Zero-trust AI integrations can be built on lean, cost-effective serverless architecture—Cloudflare Workers, signed webhooks, and audit-logged spreadsheets—without paying for enterprise middleware or risking company data.
Why This Exists
Custom GPTs and AI assistants have become the default interface for internal team workflows: searching product notes, checking inventory, sorting lead emails, and finding company policies.
Most teams connect their data using off-the-shelf plugins or direct account links for Google Drive, Notion, and spreadsheets. Because the setup screen looks official, teams assume it is safe.
It isn’t. Off-the-shelf connectors grant the language model direct write permissions to your live files. When an employee asks the assistant in chat to “clean up outdated contacts” or “update customer rates,” the model executes raw write commands straight against your master rows. There is no intermediate staging, no pre-flight diff, and no safety gate. A single misunderstood column or an indirect prompt injection in a customer email can overwrite formulas with flat text, delete records, or apply edits to the wrong client.
Our API-Connected GPT system establishes a zero-trust perimeter between the AI model and your internal databases. Every request is verified by an edge gateway, validated against strict schemas, stripped of personal data, and authenticated with cryptographic signatures. The AI only ever performs the exact business tasks you allow.
The Reality
Authorizing a standard Google Drive or spreadsheet plugin inside a chat tool gives an unpredictable model direct write access to your actual files. Prompt rules like “be careful not to delete formulas” offer zero perimeter defense.
An AI should never hold direct database mutation credentials. Our edge gateway acts as an isolated holding tray—the assistant can only submit draft proposals to a staging queue, leaving company records physically protected until a person on duty clicks “Approve.”
Small-Business Application Scenarios
Four workflows where teams use this safely.
This architecture connects conversational assistants to everyday business tools while guaranteeing that the AI can only draft proposals—never execute irreversible database actions without human review.
Lead & Inquiry Intake
Sales, Agencies & Real Estate
An employee or customer pastes a messy email, call transcript, or web inquiry. The assistant checks your service catalog and drafts a structured lead record with company name, project scope, and urgency.
The AI cannot send emails, update pipeline deal stages, or alter existing client records. It only creates an intake proposal for human sales review.
Customer Support Triage
E-Commerce, Services & Software
Reads incoming client questions, checks your knowledge base for approved answers, and creates a categorized ticket with urgency tags and affected office locations.
The AI cannot close tickets, issue refunds, change contracts, or view other customers’ private accounts. A duty manager reviews and assigns the ticket.
Quote Request Preparation
Trades, Studios & Manufacturers
Compares customer project requirements against your pricing rules and inventory lead times to draft an itemized estimate with listed assumptions.
The AI cannot grant unapproved discounts, promise delivery dates, or issue a binding quote without owner sign-off. It only prepares the draft.
Internal Policy & Handbook Lookup
HR, Operations & Hospitality
Gives staff fast, conversational answers across employee handbooks, property check-in procedures, vendor agreements, and compliance guidelines.
Strictly read-only. The AI has zero write routes to alter company policies, disclose employee salary data, or leak access codes.
Challenging Our Own Claims
What we assumed, what we tested, and what actually broke.
Connecting an AI to a spreadsheet is easy in a demo video. Making sure it cannot corrupt master data, hallucinate parameters, or leak private records in production is where naive setups fail. Here are four real breakdowns from our test harness, and how we engineered defenses around them.
The Prompt Boundary Fallacy
Why conversational instructions are not a security firewall
The Two-Tier Write Invariant
Why off-the-shelf spreadsheet connectors are an operational hazard
The Idempotent Replay Trap
What happens when networks take 4 to 6 seconds to respond
Cryptographic Gateway Isolation
Why Bearer API keys alone leave internal backends exposed
Live Working Proof
Tested on the Czech job market.
We implemented this architecture for the Czechia Expat Job Scout: a custom GPT connected to a 50+ source database through a Cloudflare Worker gateway with zero CV storage and human-reviewed discovery proposals.
Verified Architecture
- Custom GPT with OpenAPI 3.1 action specification
- Cloudflare Worker edge gateway with HMAC-SHA256 signing
- Append-only proposal queue with full audit log
- Zero PII/CV retention and GDPR compliance policy